Agile Threat Modeling
Evaluating software architectures against security risks and creating mitigation advice in an agile and interactive fashion.
Attack Tree Quickstart
Get an initial attack tree with security controls for your product or architecture — fast and async, no workshop required.
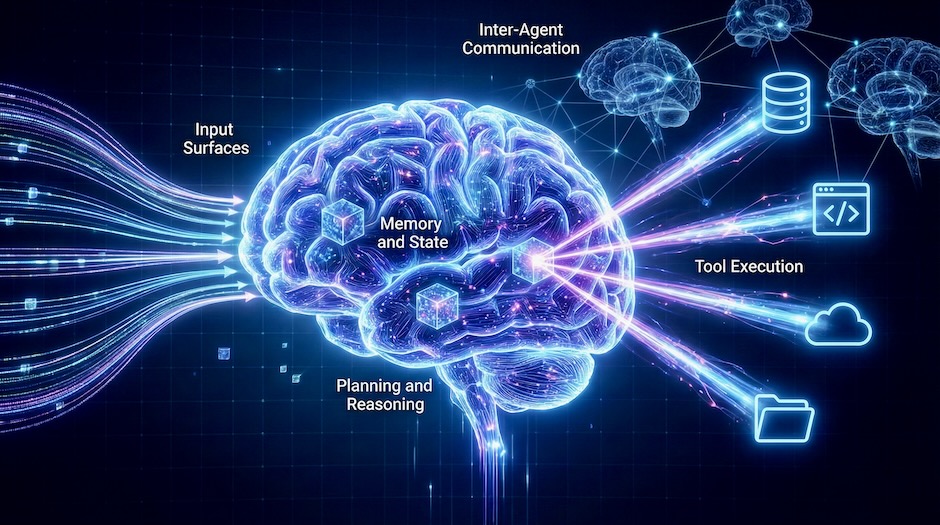
Agentic AI Security
Threat modeling for agentic AI systems — tracing attack paths across input surfaces, reasoning, tools, memory, inter-agent communication, and the agent supply chain.
Coding Agent Security
A two-session assessment for the secure use of AI coding agents like Copilot, Cursor, Claude Code, Kiro, and Codex, including MCP and AI gateways, with a nine-month roadmap.
Security Sparring Partner
Ongoing security advisory retainer: regular check-ins, architecture reviews, ad-hoc questions, and priority booking for better security decisions. Alternatively: a Security Contingent with consulting days callable over 12 months.
Security Architecture
Security review of software architectures and system designs, including zero trust architecture assessments — defining a roadmap for improvement and hardening.
DevSecOps Pipeline
DevSecOps coaching for AppSec build pipelines — security scan automation, AI-powered code review integration, securing AI-assisted development, and false positive handling.